Native on iPad and Mac.
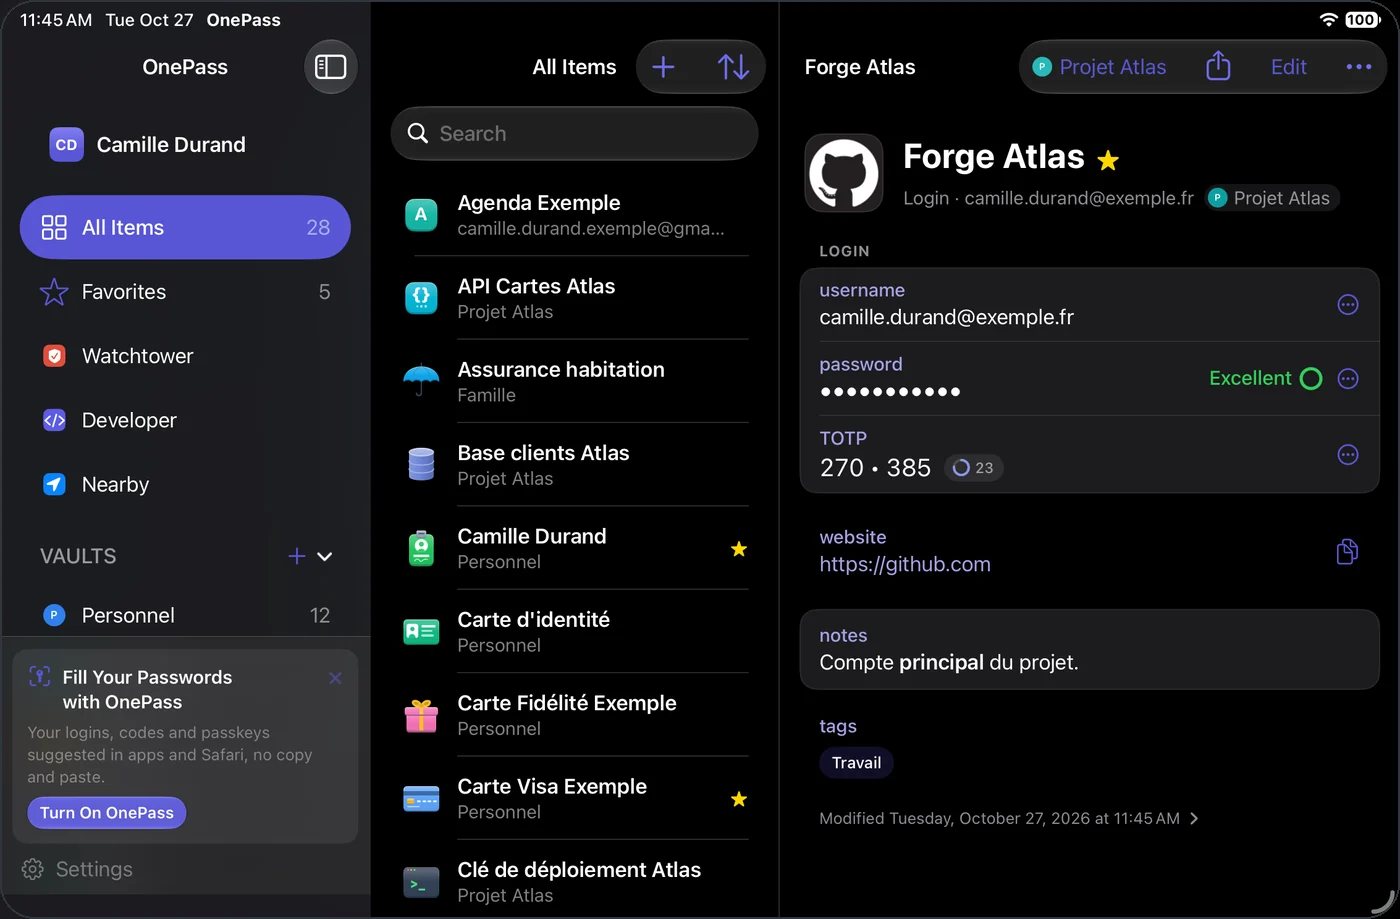
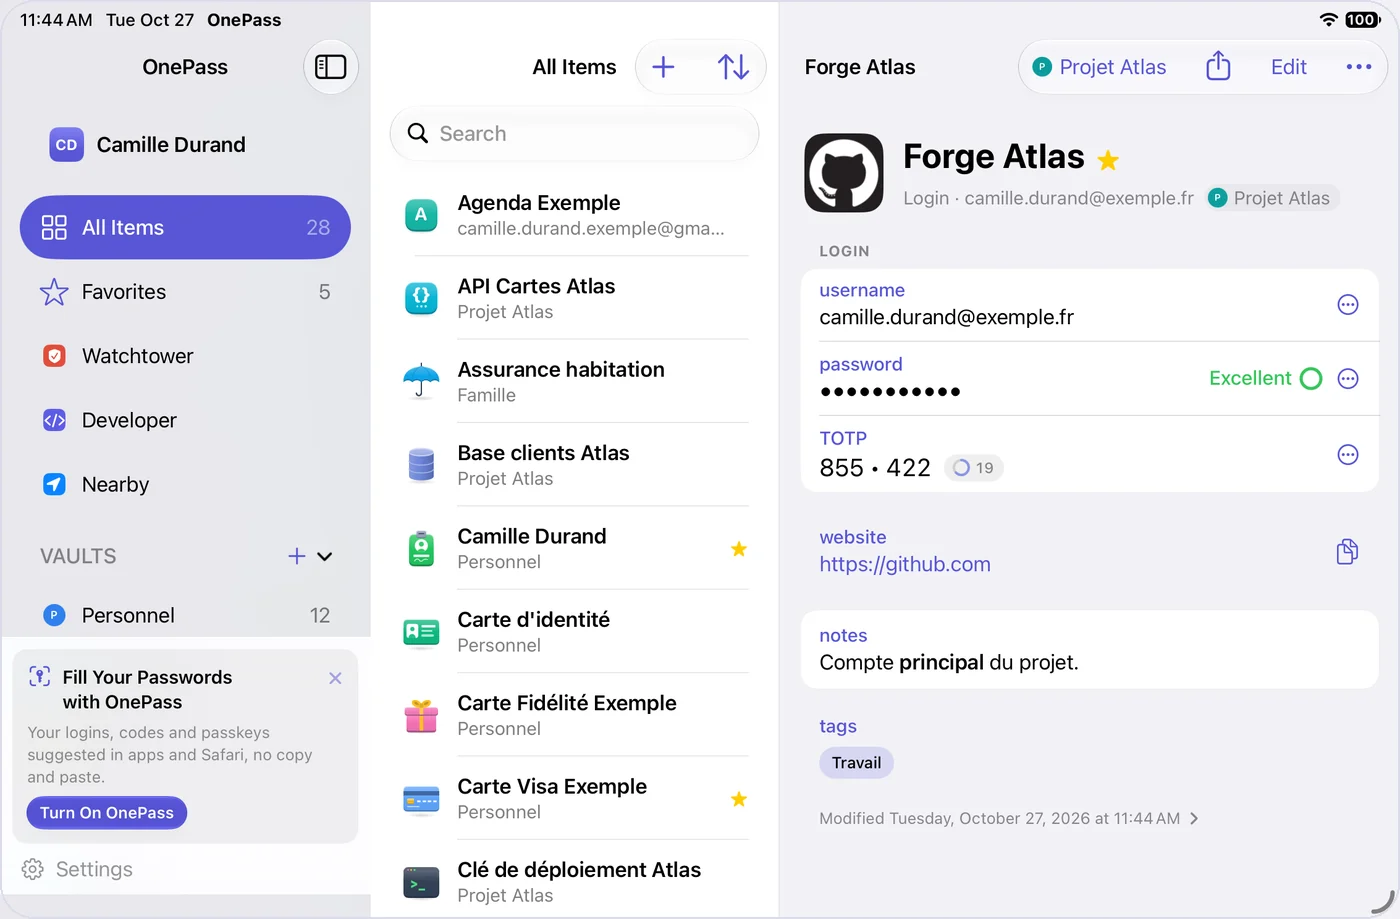
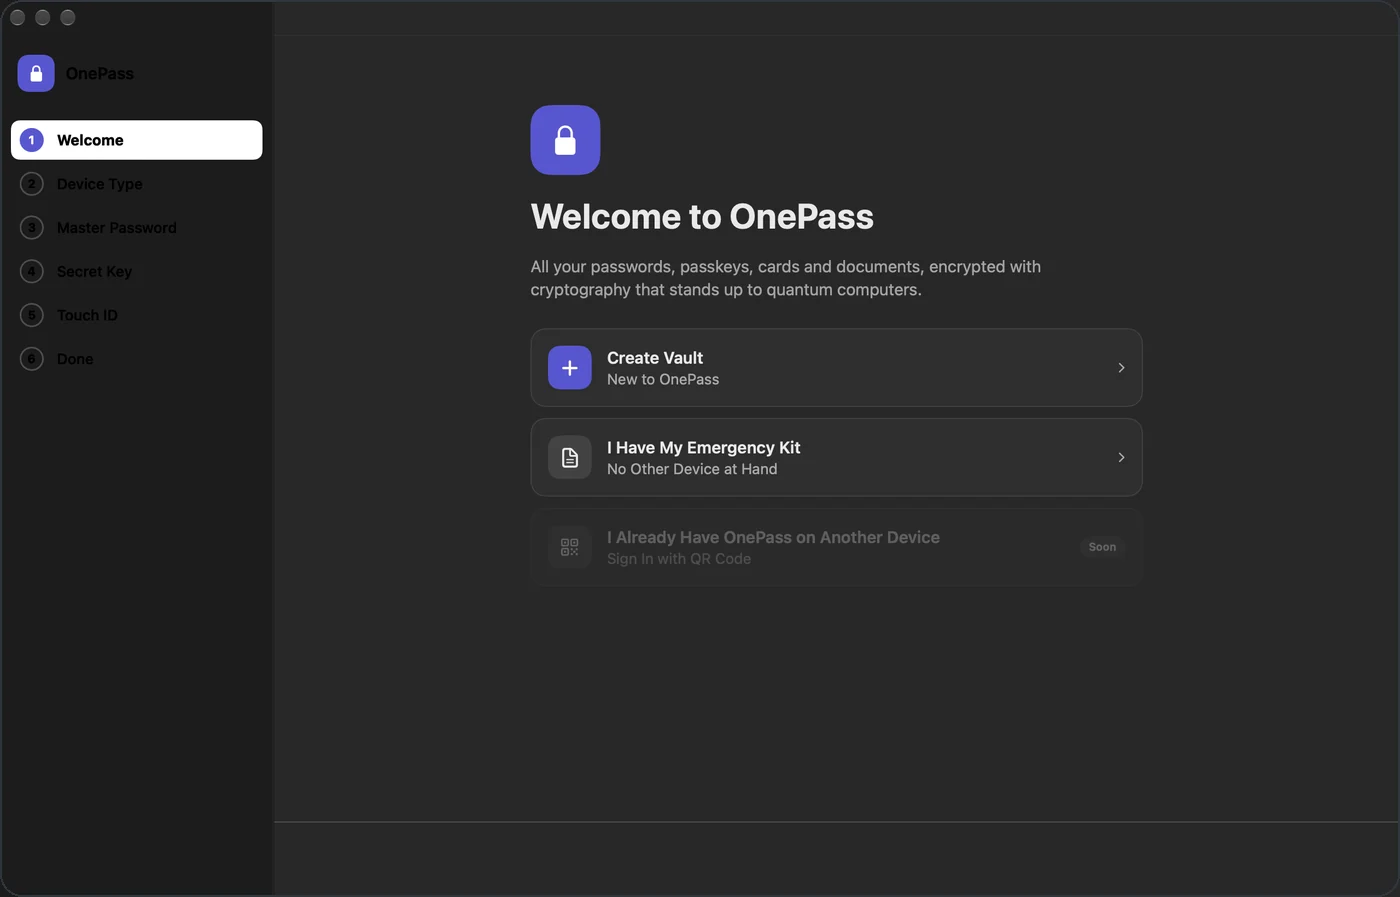
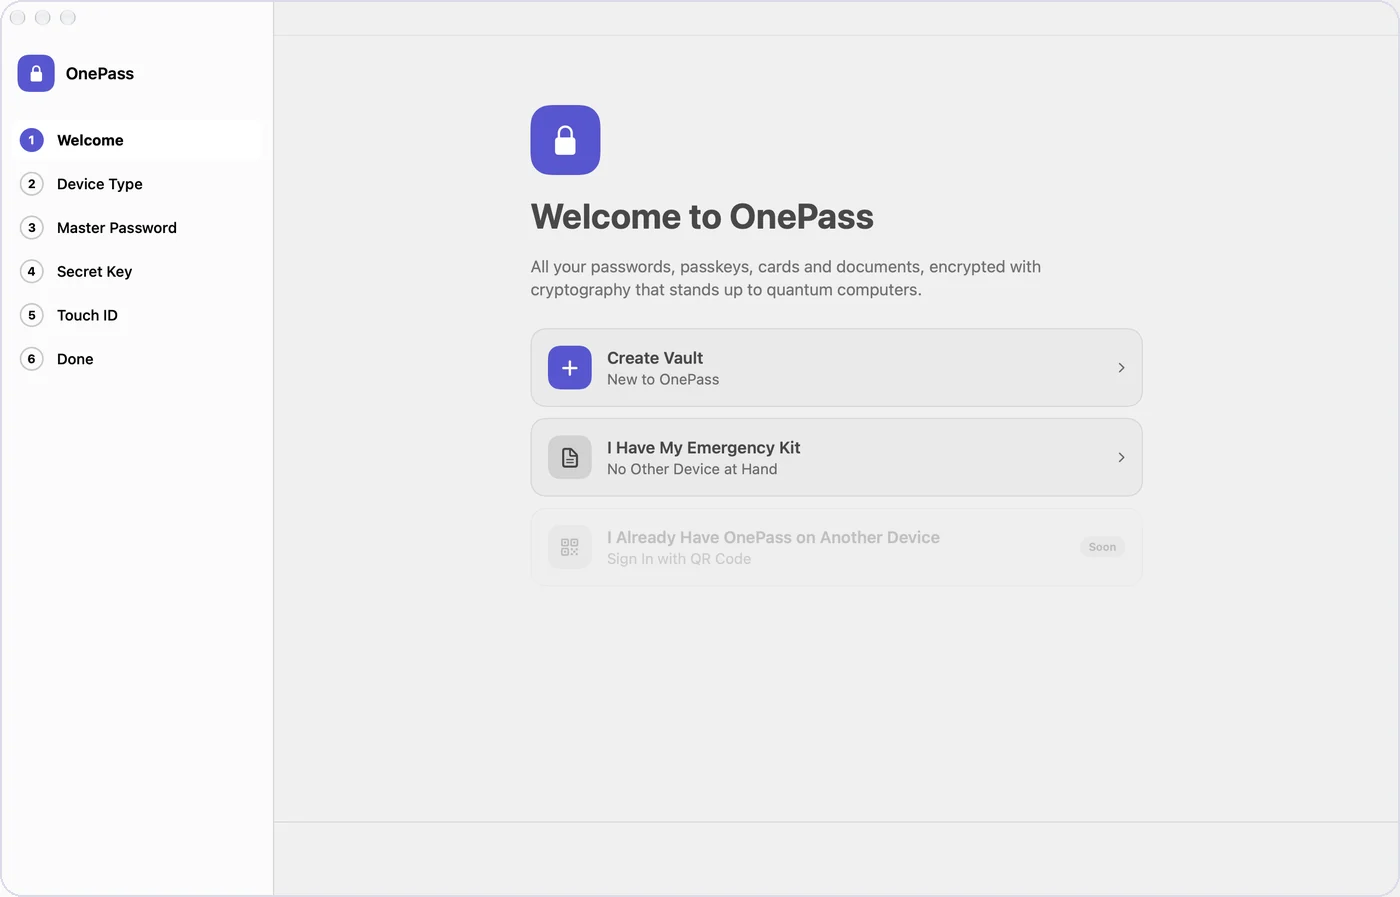
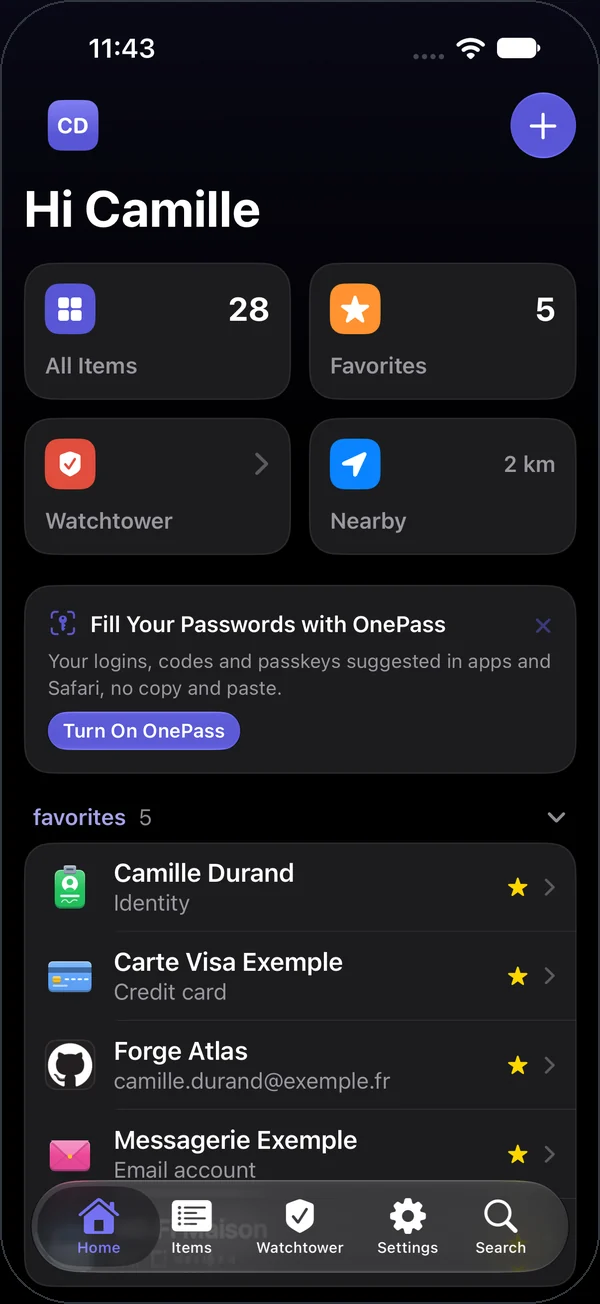
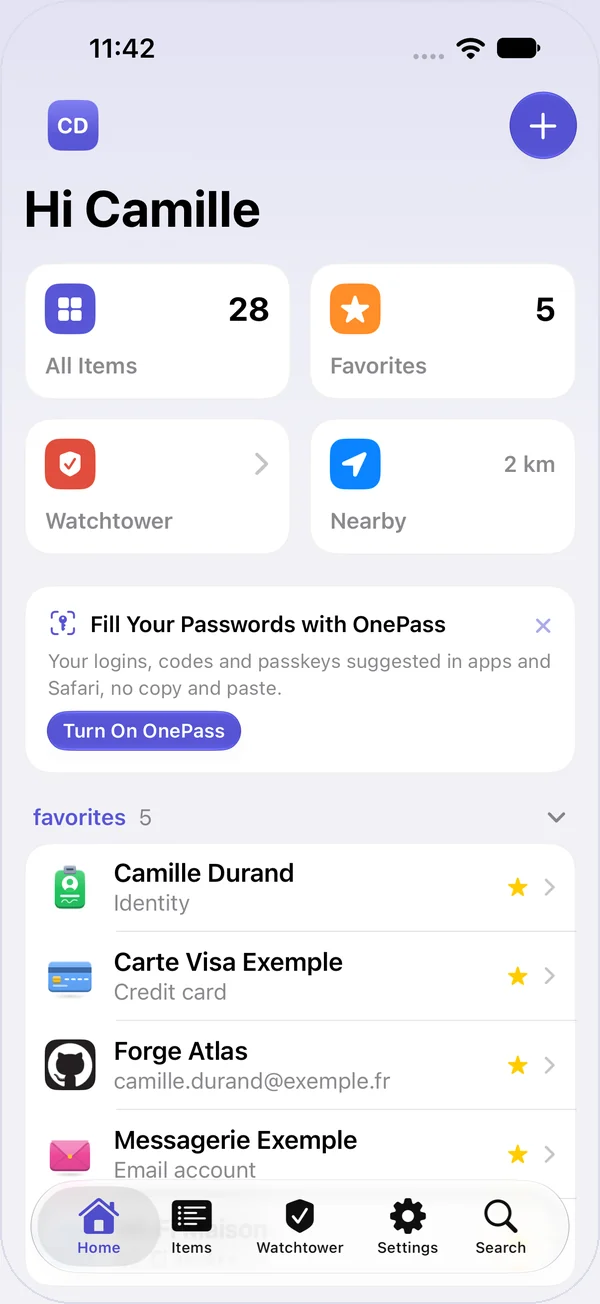
One SwiftUI app for iPhone, iPad, Mac and Vision Pro. Three columns on iPad, and a real Mac app that isn't a ported iPad one.
 OnePass
 keeps your passwords, passkeys, cards and documents on iPhone, iPad, Mac, Apple Watch and Vision Pro. Its keys are wrapped with post-quantum encryption, and the storage that syncs them only ever holds ciphertext. It's free and the code is open.
OnePass is pre-release software (v0.2). It hasn't had its external security audit yet, so please don't keep real secrets in it until the first audited release.
iPhone, iPad, Mac, Apple Watch, Vision Pro and a browser extension
A native app on every Apple device, with one Rust core underneath that does all the crypto.
26 item types, from logins and cards to passports, SSH keys and crypto wallets. Several vaults, favorites and fast search.
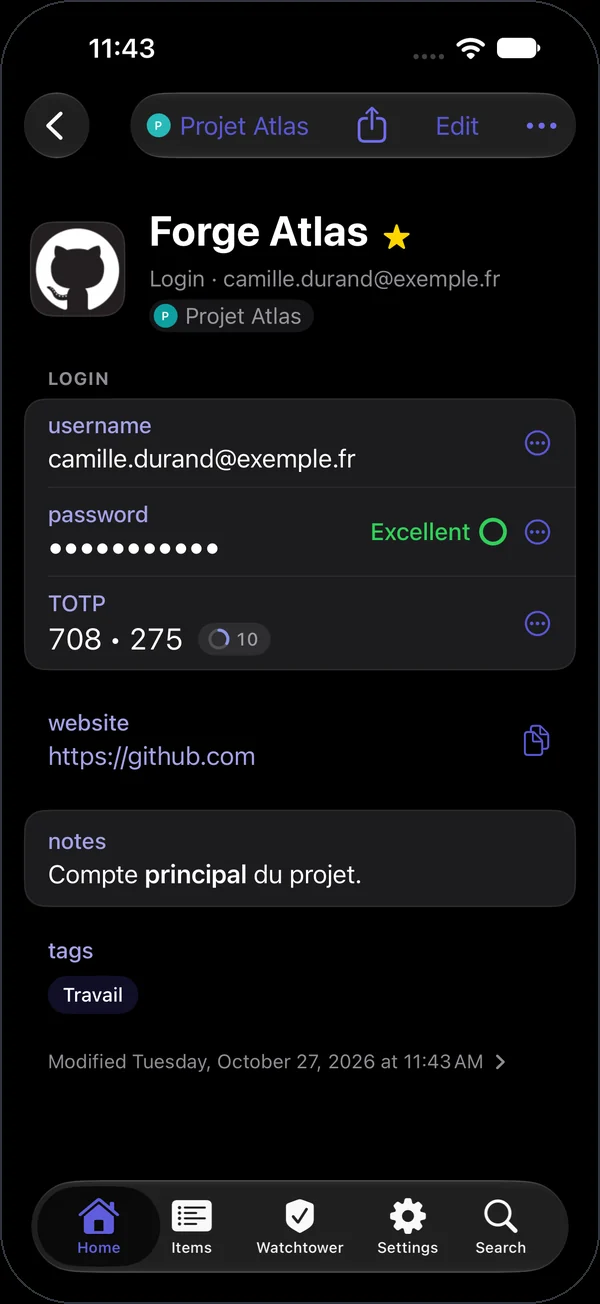
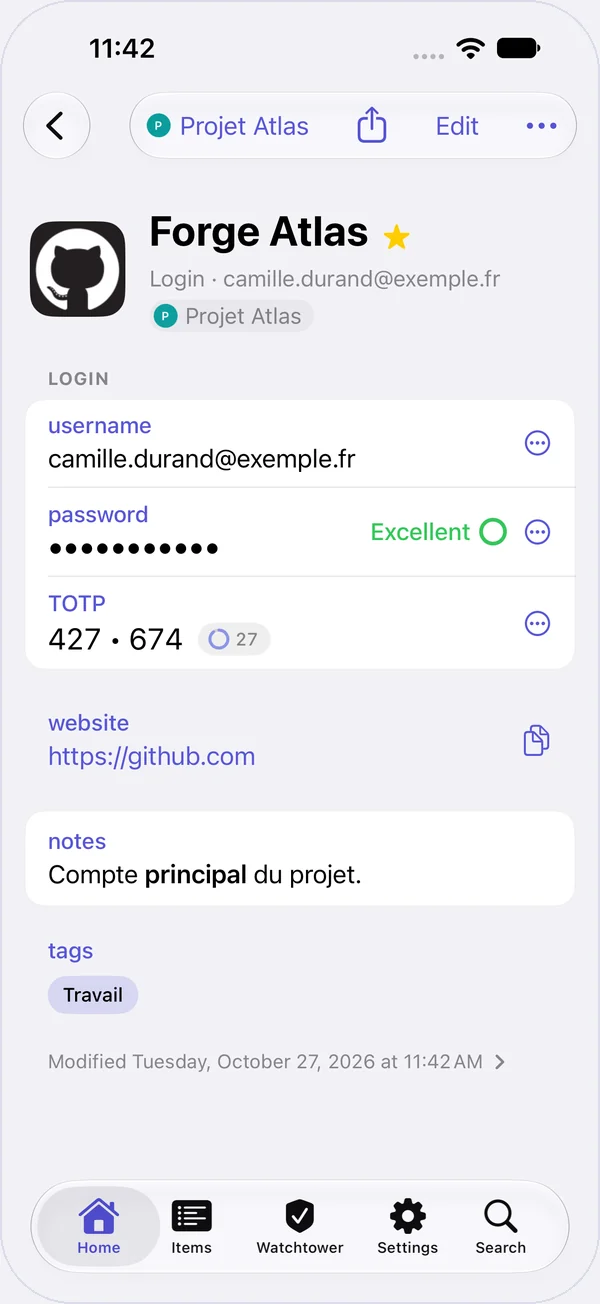
A login holds its password, its one-time code and its passkey. Passkeys are made and used inside the Rust core, and the private key never reaches the app's Swift code.
Your key comes from your master password and a 256-bit Secret Key made on your device. A copy of the sync data is no use to anyone without both.
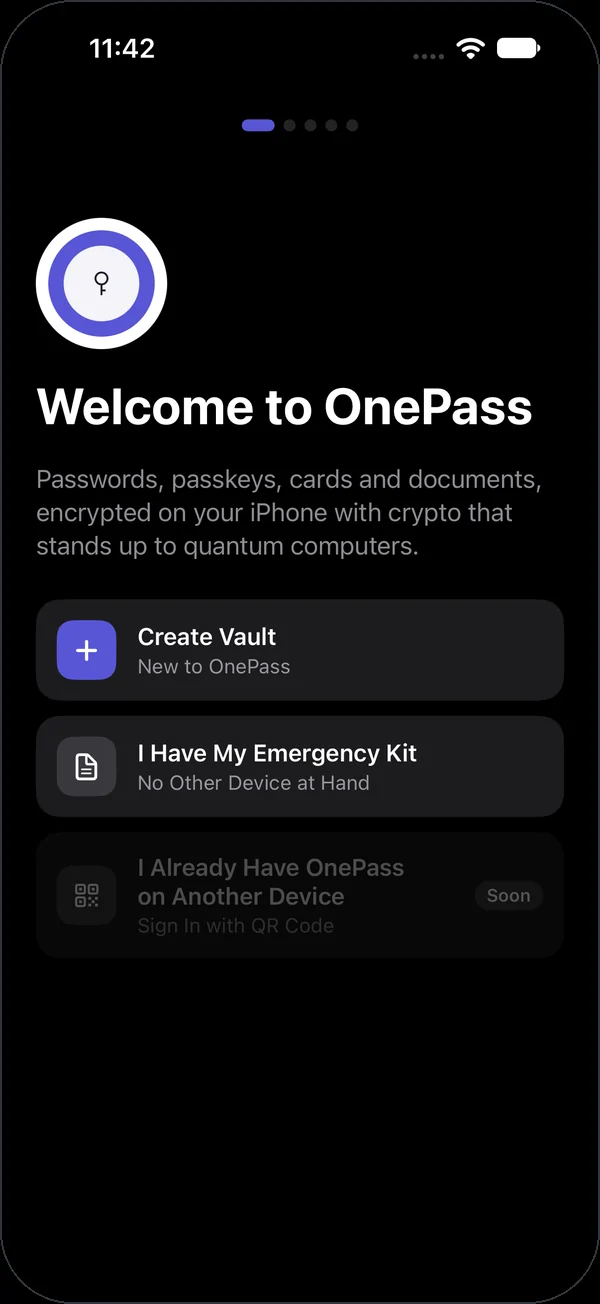
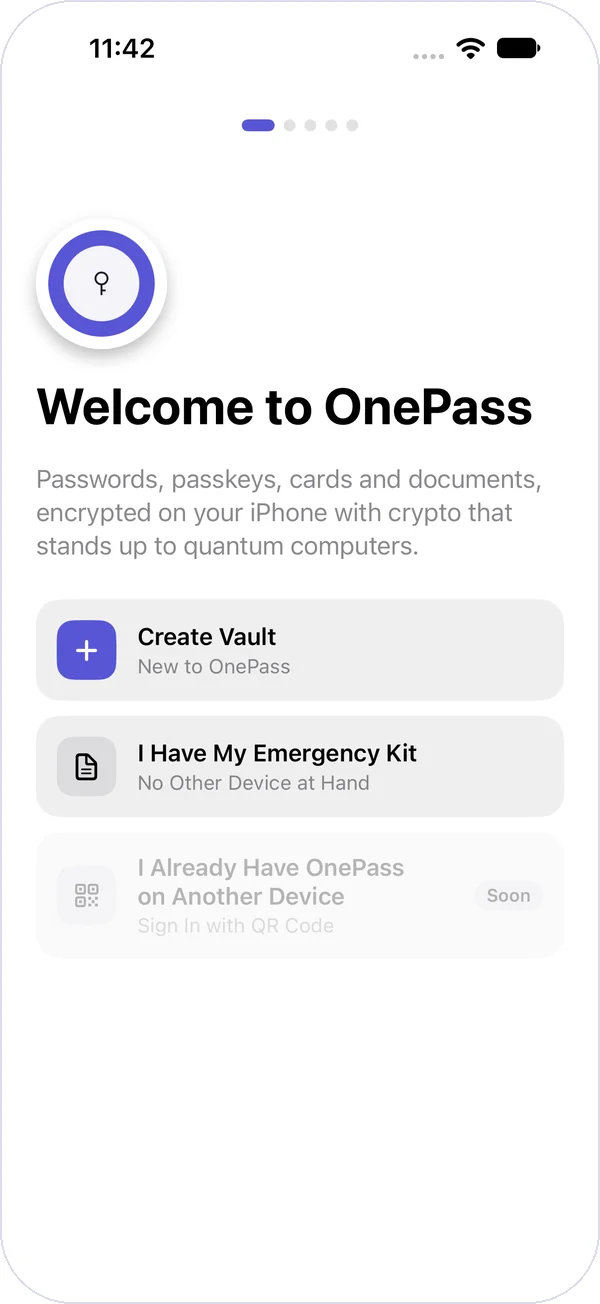
One SwiftUI app for iPhone, iPad, Mac and Vision Pro. Three columns on iPad, and a real Mac app that isn't a ported iPad one.
Screenshots show fictional demo data.
Every vault carries a signed, hash-chained manifest. If a broken or malicious sync backend rolls back, forks, drops or swaps an item, the app knows before it uses anything.
Vault keys are wrapped with ML-KEM-1024 and X25519 together. Manifests and backups are signed with ML-DSA-87 and Ed25519, and both signatures have to check out. Your account identity is an SLH-DSA key.
End-to-end encrypted sync over CloudKit, in your private iCloud database. Apple's own encryption is a bonus. The threat model assumes it fails, so storage only ever sees padded ciphertext.
Each attack class from the 2026 ETH Zurich and USI study of cloud password managers is replayed by a hostile server test suite in the repository.
A PDF with your Secret Key and a QR code, made on your device, so a new phone can get back in.
The rest of what's in v0.2.
System AutoFill on iPhone, iPad and Mac, with QuickType suggestions and one-time codes filled into verification fields. It saves new passwords and suggests strong ones on iOS 26.2 and later.
For Chromium browsers, Firefox and Safari. It pairs with the app by a 6-digit code you compare on both screens, talks to it over a post-quantum encrypted channel and only fills HTTPS pages.
Weak, reused and old passwords, breached sites, and sites where you could turn on 2FA or passkeys. Leaked passwords are checked with Have I Been Pwned's k-anonymity, so only a 5-character hash prefix leaves the device.
A standalone, read-only Watch app for your codes, with complications. It holds at most 50 items and never login passwords, card codes, PINs or notes. Widgets, Controls and Shortcuts on iPhone.
A CLI, an SSH agent that asks before every signature, and an MCP server so an AI agent can use a credential without ever seeing it. Each request waits for your approval and goes into a signed audit log.
21 formats in, from 1Password, Bitwarden, LastPass, Dashlane, Proton Pass, KeePass, the browsers and FIDO's Credential Exchange. Export goes to a signed, encrypted archive.
Take vaults off a device before you cross a border, and bring them back after.
Strong passwords and passphrases from the EFF word lists.
The tests are in the repository, next to the code they check.
aws-lc-rs runs against libcrux in differential tests, with property tests on the AEAD.
ProVerif models of account creation and unlock, vault manifests, the Emergency Kit and the extension bridge, including runs where one half of each hybrid KEM is broken.
Hundreds of seeded, fictional websites served locally, to measure how often the extension fills a form and whether anything ends up where it shouldn't.
We'd rather you know before you build it.
One is planned before the first stable release. Until then, please don't store real secrets in OnePass.
To try it today you build it from the repository. The dev CLI and the dev native messaging host keep secrets in a form meant for development only.
A self-hosted server is planned after v1. Sync on real iCloud, across two devices, still has to be checked by hand.
The Safari extension ships inside the Mac app, in Debug builds only until the app serves the bridge.
Sharing, organizations, a web app and recovery codes are on the roadmap for later.
A device taken over at the OS level, or an attacker who can read the app's memory. Secrets are zeroized, and memory locking isn't in yet.
The Rust core needs Rust 1.99.1, the apps need Xcode 27 and XcodeGen, and the extension needs Node 22. The apps target iOS 26, iPadOS 26, macOS 26, watchOS 26 and visionOS 26 or later.
CloudKit sync is only compiled into the signed Release-CloudKit configuration, which needs your own Apple Developer team and iCloud container.
OnePass is licensed under the GNU Affero General Public License v3.0 or later. For a commercial license without the AGPL terms, write to security@somalabs.me with License in the subject.
Please report it privately through GitHub Security Advisories or to security@somalabs.me, never in a public issue. Reports are acknowledged within 72 hours.
Report privatelyContributions are welcome, and reviews of the crypto and the threat model most of all.
Contributors sign a contributor license agreement once, before their first pull request is merged.